By: Natalie Johnson
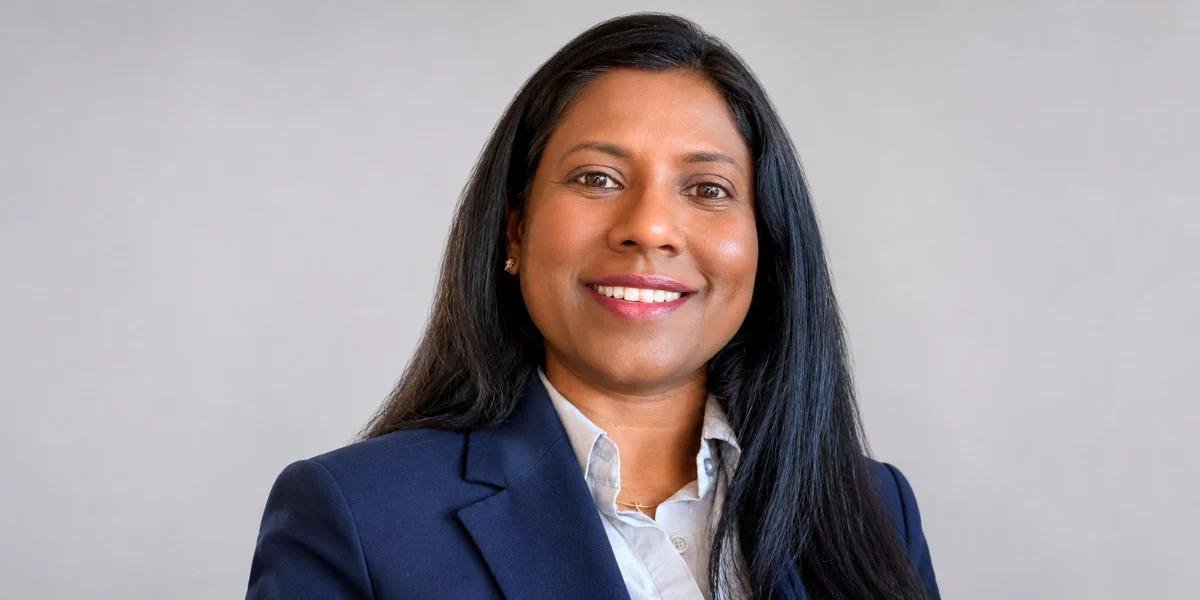
Companies that deploy AI have often written their principles down. Far fewer can tell you what their models are doing in production right now, which systems they can reach, or who answers for it when something goes wrong. That gap between the policy document and the running system is where trust either gets built or quietly destroyed, and it is widening fastest in exactly the places where mistakes cost people the most. Anu Ramraj, who leads Vaultzy, argues that responsible AI is not a governance layer sitting above the product. It is the reason a company gets to ask for trust at all, and companies handling identity, health, finances, legal rights, or government benefits have the least room to treat it as anything else.
Consequential Decisions Change The Engineering Requirements
Ramraj grounds her definition in the National Institute of Standards and Technology (NIST) AI Risk Management Framework: AI that is valid and reliable, safe, secure and resilient, accountable, explainable, privacy-enhanced, and fair. What matters is where she applies it. The people Vaultzy serves include underserved communities who carry the most exposure and the least margin for error when a system fails. A misfiled benefits application. A lost immigration record. Those are not edge cases to be absorbed by an accuracy percentage; they are the outcomes that define whether the product works. “Responsible AI means the system is accountable, explainable, and auditable by design, not just accurate on average,” she says. “If I can’t tell a user why the AI guided them along a particular path with their document, and guarantee their privacy along the way, I haven’t earned the right to call the company trustworthy.”
That reframing has teeth, because it moves a whole category of concerns out of legal review and into the engineering backlog. “In those situations, accuracy, privacy, security, transparency, and human agency aren’t simply compliance requirements. They are product requirements,” Ramraj says. The test she applies is deliberately narrow: does the AI help someone make a better decision without taking that decision away from them? Can they understand it, correct it, and control their own information? Plenty of AI products fail that test while scoring well on benchmarks, because they optimize for the system’s confidence rather than the user’s comprehension. Her position is that capability without boundaries is not a feature. “Just because AI can do something doesn’t mean it should do it without boundaries,” she says. “Trust has to be earned.”
Separating Intelligence From Authority
The most consequential architectural idea Ramraj advances is a split that most AI roadmaps blur: intelligence and authority are different things, and they should not live in the same place. AI helps people understand and act on information. Blockchain-backed records establish trust in the information itself: creating a tamper-evident, independently verifiable record that a document passed through an authorized human process, whether a notary validating a transaction or an administrator issuing a document. At Vaultzy, AI can organize vital documents, identify what is missing, flag an expiration, or guide someone through a life event. What it does not do is certify. “AI can understand, assist, recommend and take specifically permitted actions, while independent mechanisms establish identity, consent, provenance and verification,” she says.
The reasoning behind that split matters more than the implementation. Ramraj connects it to an idea she calls the “Human Premium,” from her book When AI Robots Knock. As AI takes on more of the generating and executing, the uniquely human value migrates toward judgment, accountability, and who is willing and authorized to stand behind the work. Documents with legal or institutional weight demand a higher level of assurance than an ordinary AI interaction can supply, and no amount of model improvement closes that particular gap. “AI may increasingly do the work, but trust comes from knowing who authorized it, who verified it, and who ultimately stands behind it,” she says. Companies racing to hand agents ever broader authority are betting against that distinction. Ramraj believes it becomes more fundamental as autonomy increases, not less.
Treat Agents Like Workers, Then Measure Them Like Workers
Ask Ramraj where industry governance is weakest, and she does not point at missing frameworks. AI principles, committees, and responsible-AI leaders now exist in plenty of organizations. The failure is downstream. “We have become reasonably good at documenting what AI is supposed to do. We need to become much better at measuring and reporting what AI is doing.” The operational questions are the hard ones:
- What models and agents are running?
- What data can they access?
- What decisions can they influence?
- What actions can they take?
- How often can humans override them?
- What failures occur and who is accountable?
Her conclusion is blunt and should unsettle any board reviewing an AI policy deck. “Accountability needs telemetry, not just policy.” What follows is evidence-driven governance: agent inventories, continuous monitoring, audit trails, incident reporting, permission tracking, outcome measurement, and clear ownership.
Her proposed model borrows from something companies already know how to do. Organizations know who their employees are, what roles they hold, who they report to, and what systems they can touch. Agents should be answerable to the same questions, with a job description, defined access, approval limits, supervision, and performance expectations. Ramraj would formalize it as an AI Agent Code of Conduct: protect confidential information, operate only within delegated authority, identify themselves appropriately, communicate uncertainty, never circumvent controls, escalate consequential decisions to humans, and maintain an auditable record of significant actions. Underneath sit three principles, identity, authority, and accountability, with least privilege applied so an agent holds only the authority its specific job requires. “An agent that can read a document, for example, should not automatically have the authority to modify or share it.” The lesson she draws is one the security industry already paid for. “We need to treat responsible AI the way we learned to treat cybersecurity: designed in, not bolted on.” And the metric leaders keep reaching for is the wrong one. “The goal isn’t maximum autonomy. It’s appropriate autonomy, with clear roles, clear boundaries, and human accountability.”
Follow Anu Ramraj on LinkedIn for more insights on responsible AI, agentic governance, and building trustworthy technology.